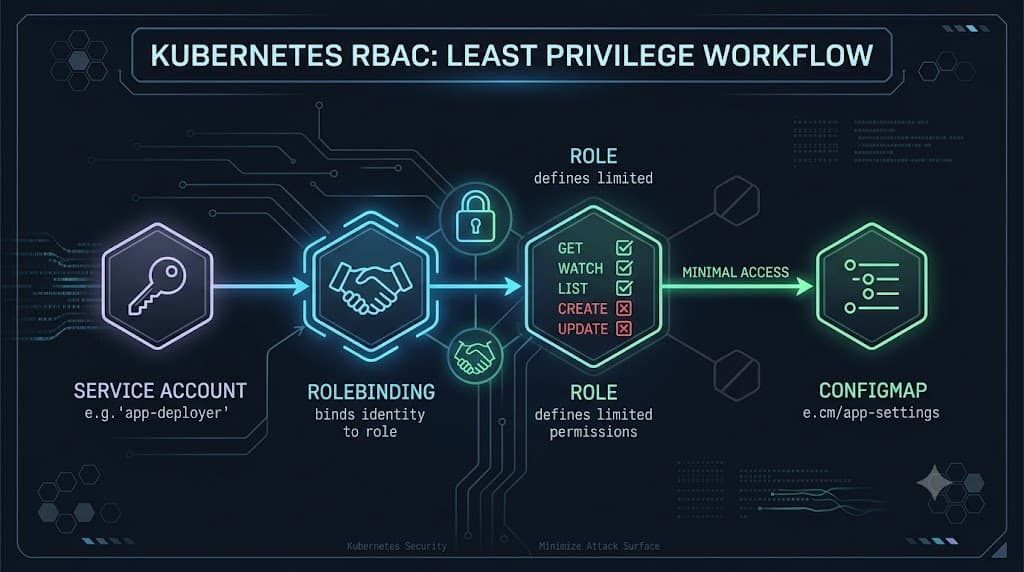
Hari 38: RBAC Auditing — Dedicated SA Least Privilege
Audit RBAC dengan krew (who-can, access-matrix). Buat dedicated ServiceAccount dengan least privilege Role: get configmap only. Kubesec score 11 ke 12, Checkov 101/0.
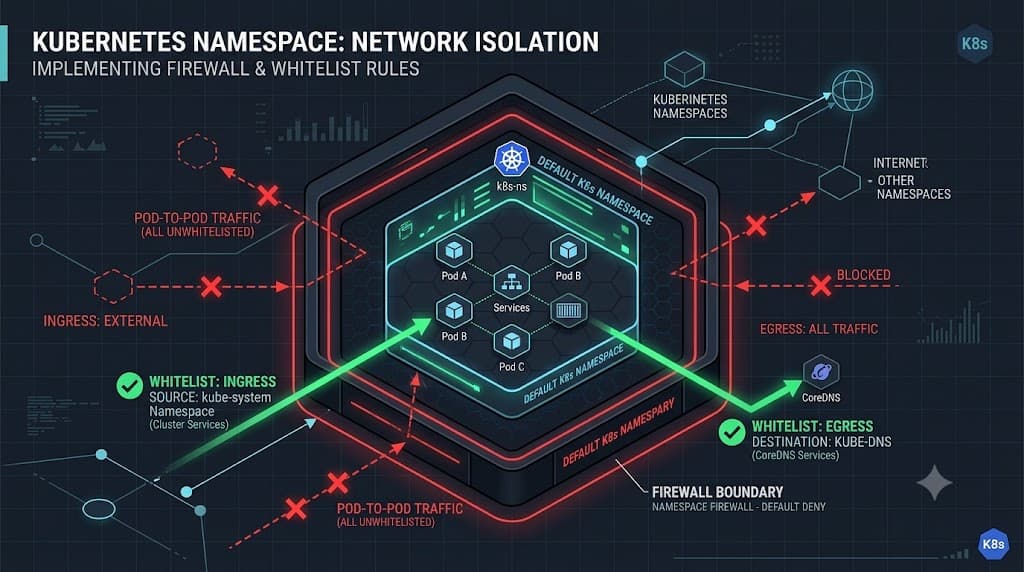
Hari 37: Network Policies — Default Deny + Whitelist
3 NetworkPolicy: default deny all ingress+egress, whitelist API dari kube-system, DNS egress. k3s flannel enforce! Cross-namespace access blocked, Checkov CKV2_K8S_6 PASS.
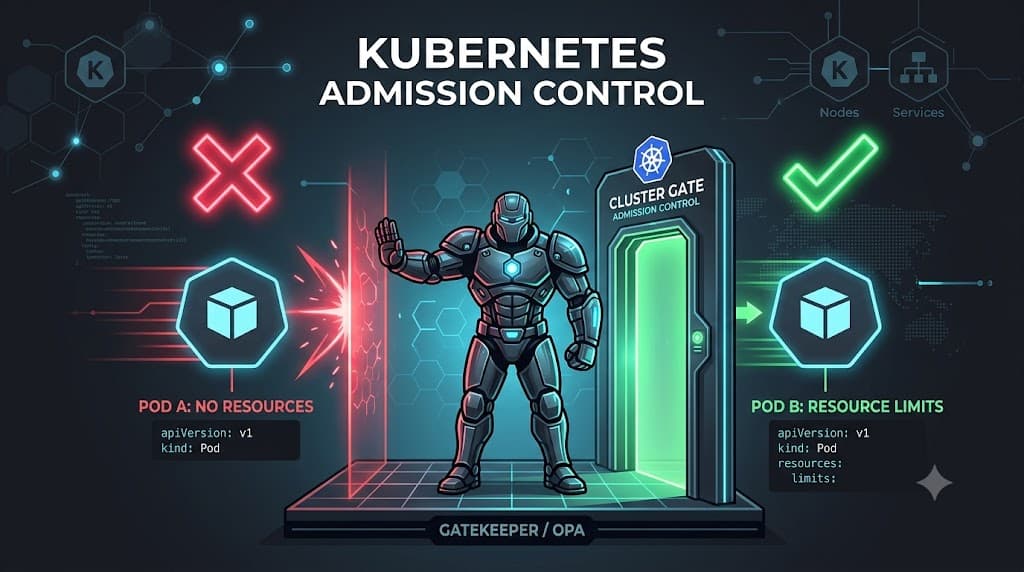
Hari 36: OPA Policy Testing — Deny vs Allow
Test Gatekeeper policy: Pod tanpa resources ditolak (4 violations), Pod dengan resources diterima. Surprise: K8s auto-fill requests dari limits sebelum webhook dipanggil.
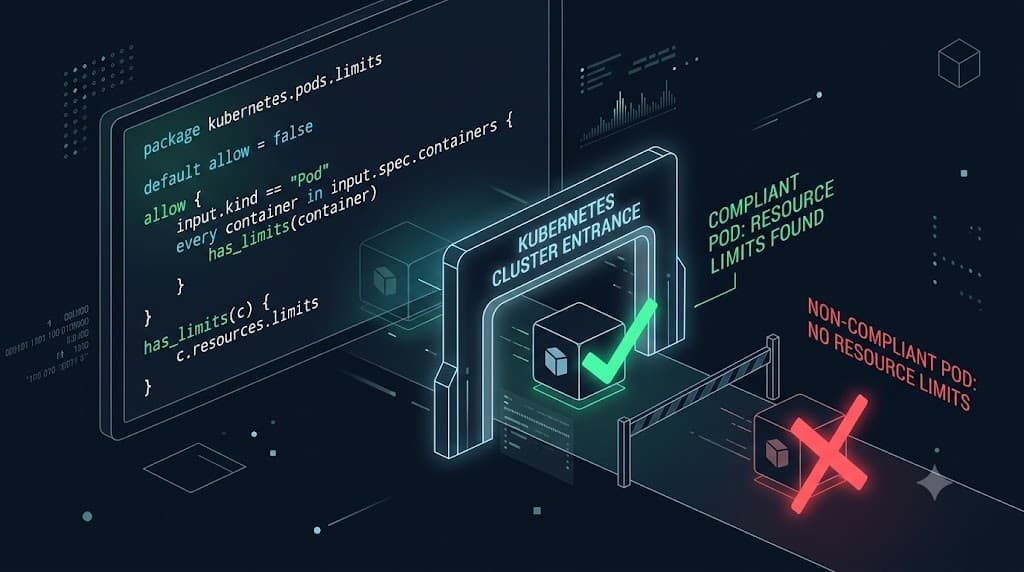
Hari 35: Rego Policy Pertama — Wajib Resource Limits
Tulis Rego policy pertama untuk Gatekeeper: Pod/Deployment tanpa resource limits dan requests ditolak. 4 violation rules, enforcementAction deny, 0 violations.
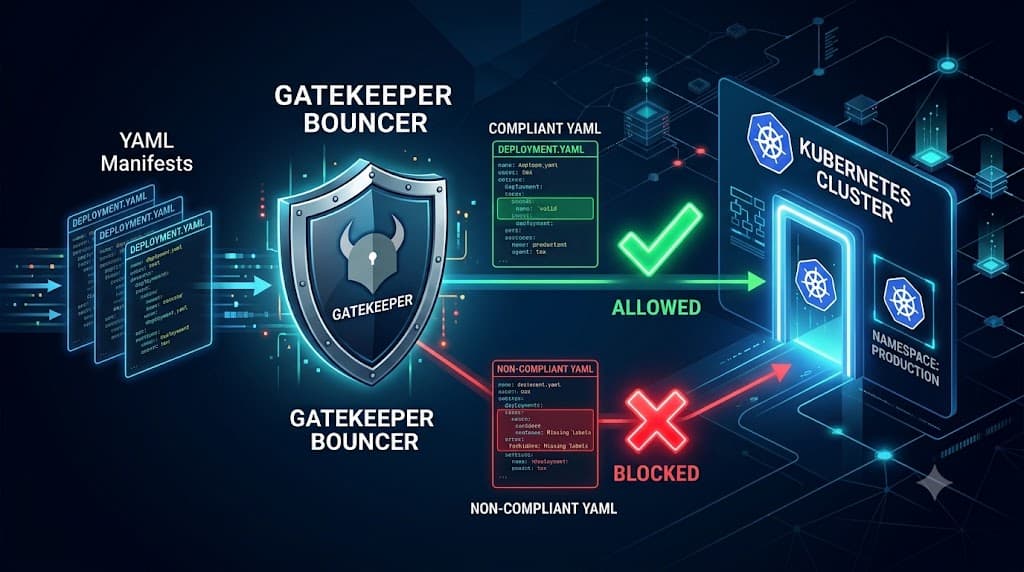
Hari 34: Install OPA Gatekeeper — Bouncer K8s Cluster
OPA Gatekeeper terinstall sebagai admission controller di k3d cluster. 2 pods running, 17 CRDs, validating webhook aktif. Besok tulis Rego policy pertama.
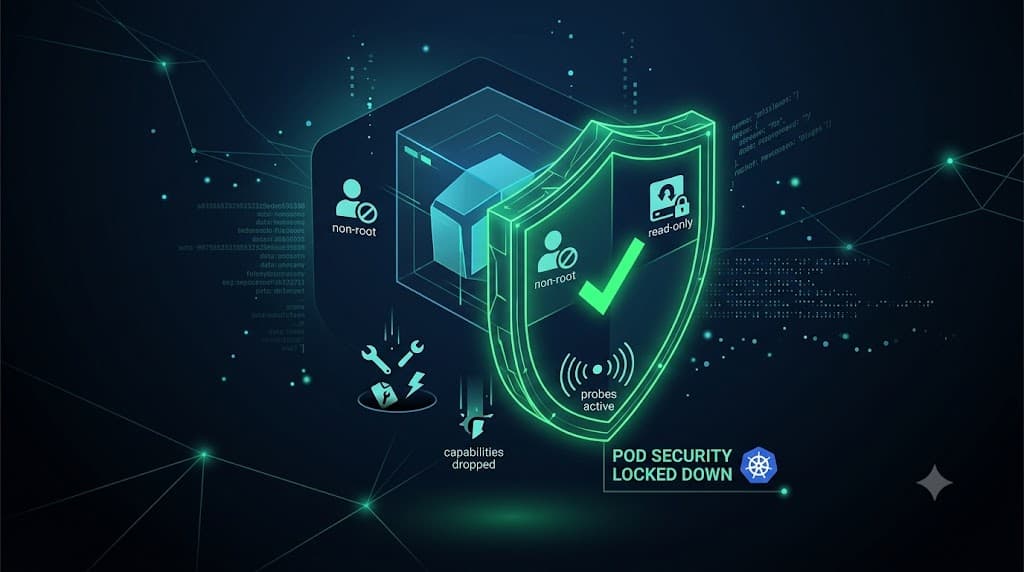
Hari 33: SecurityContext Hardening — 20 Temuan ke 0
Deployment.yaml di-hardened: non-root, read-only filesystem, cap drop ALL, probes, resources. 3 scanner: Kubesec 0→11, Checkov 20→0, Trivy 16→0. Pods tetap running.
Page 6 of 14 • 79 articles