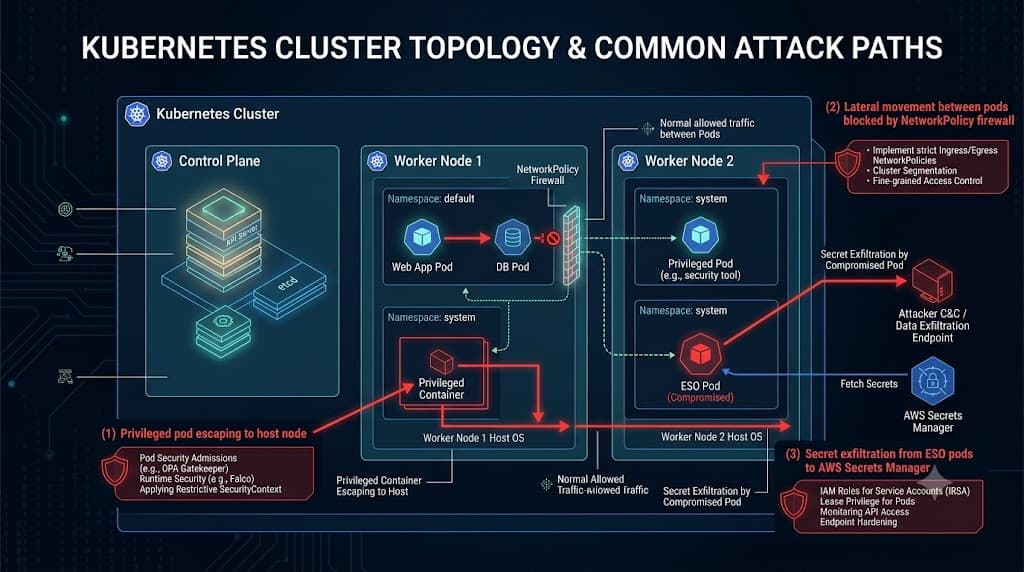
Hari 44: AI Threat Modeling — 3 Attack Paths
AI (glm-5.2) analyzes K8s cluster config and identifies 3 attack paths: container escape (CVSS 9.8), lateral movement (CVSS 7.5), secret exfiltration (CVSS 8.6). Defense in depth validated — every attack path has multiple mitigations from Day 31-43.
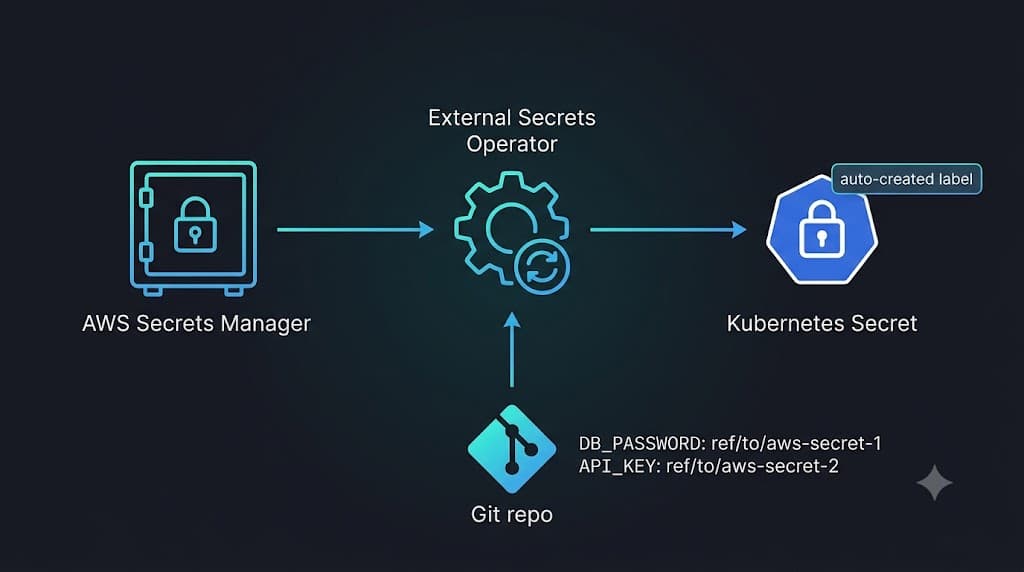
Hari 43: External Secrets — AWS to K8s Sync
External Secrets Operator sync JWT_SECRET dari AWS Secrets Manager ke K8s Secret. Secret Reference Pattern: git cuma referensi, nilai di AWS. ESO SecretSynced dalam 20s. GitHub Push Protection block Checkov report yang contain AWS keys.
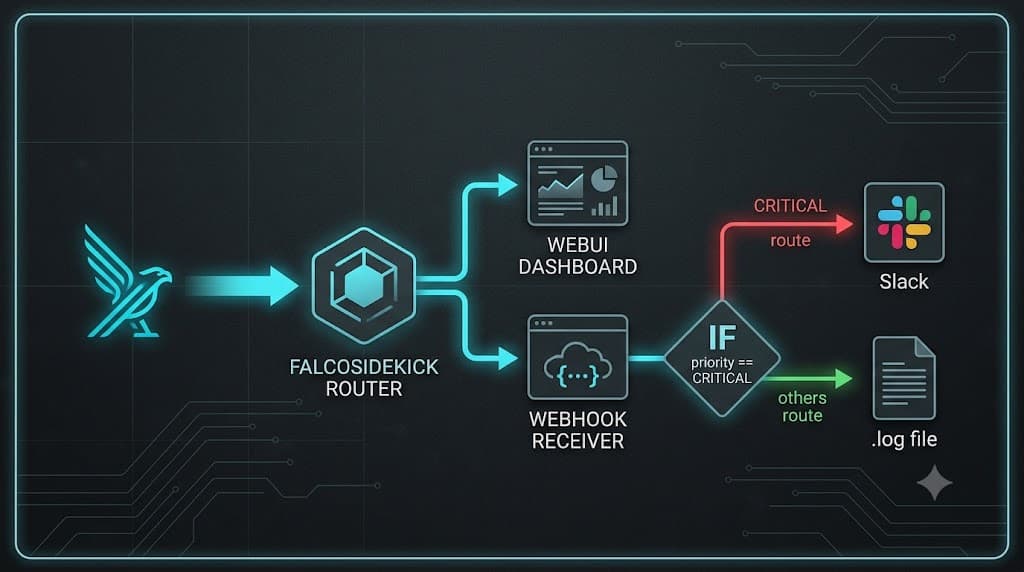
Hari 42: Webhook Alerting — Falco to Python Receiver
n8n Docker pull timed out → pivot ke Python webhook receiver. Falcosidekick webhook output enabled. End-to-end: attack → Falco → Falcosidekick → webhook → IF routing CRITICAL to Slack path. 3 alerts received.
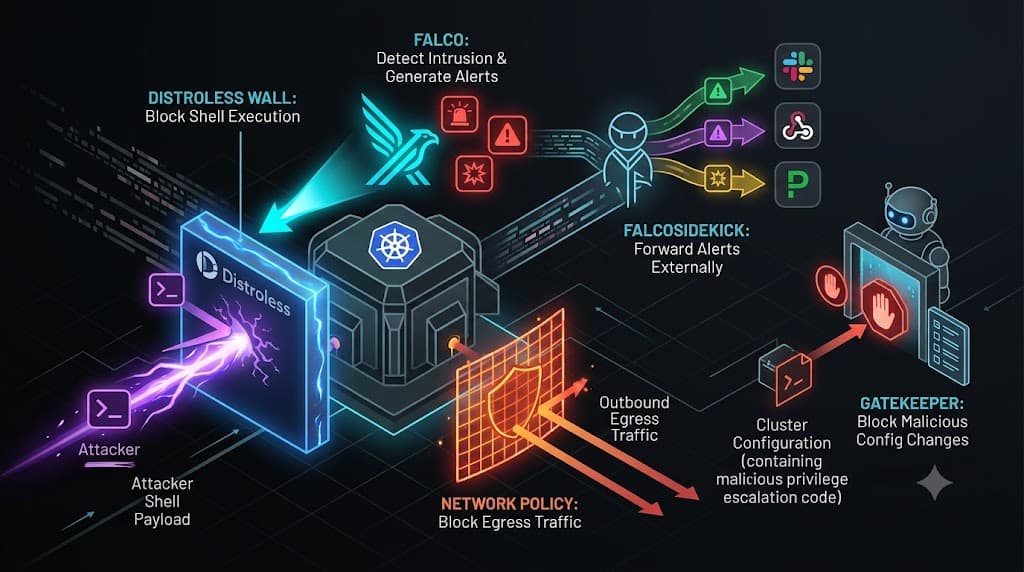
Hari 41: Falco Attack Sim — 6 Alerts, Defense in Depth
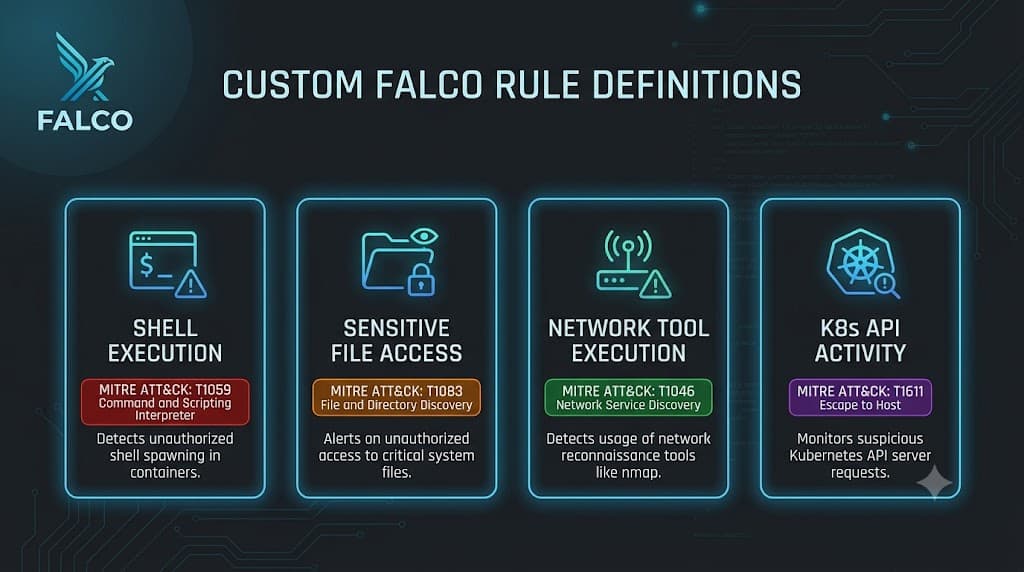
Attack simulation: shell, sensitive file, network tool, K8s API. Distroless blocks shell exec. 3/4 custom Falco rules fired (6 alerts). NetworkPolicy blocks egress. All 5 defense layers proven working.
Hari 40: Falco Custom Rules — SecureBank Detection
4 custom Falco rules untuk SecureBank: shell detection, sensitive file read, network tool, K8s API access. Helm values.yaml untuk reproducible upgrades. 29 rules total, schema validation OK.
Hari 39: Falco Setup — Runtime Security Monitoring
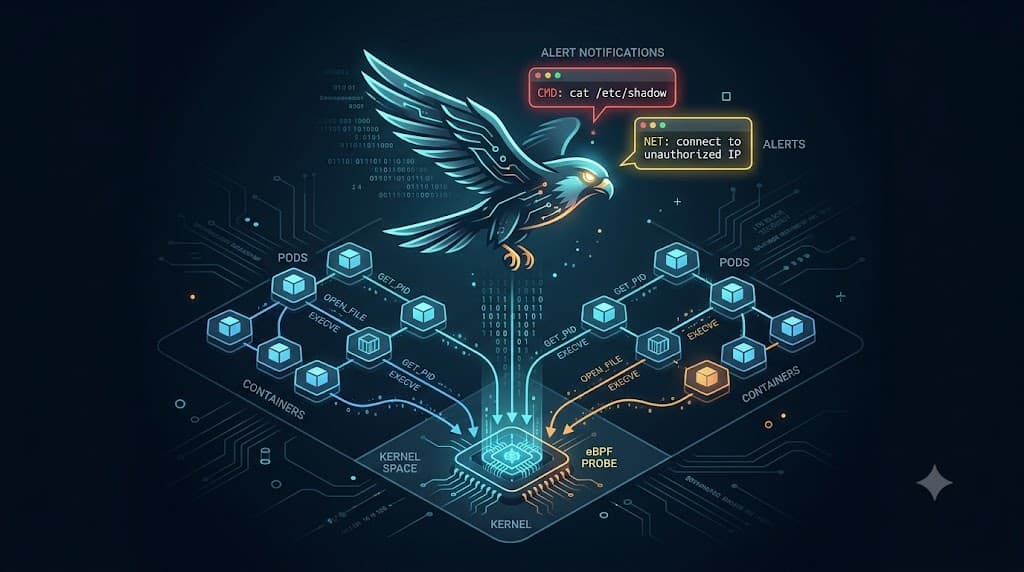
Install Falco 0.44.1 via Helm dengan modern eBPF driver. 8 pods Running, 25 default rules, alerts firing. Falcosidekick + Web UI untuk alert forwarding. Runtime detection layer.
Page 5 of 14 • 79 articles